Machine speed and
intelligence far beyond MDR.
Intelligent Defense Platform
Ask ReconSTORM
Over the past two weeks, analysts contained a phishing attempt and an unwanted program install, and confirmed three critical- and high-severity alerts as false positives. Oct 11 (Case 1004821): a phishing email from accounts@statement-notice.example.com reached j.morgan@example.com with the subject “Your Monthly Account Summary” and a malicious PDF attached. The attachment was removed and the message was quarantined. Oct 5 (Case 1004357): a user on WS-FIN-0147 ran a mislabeled “PDFHelperPro” installer, which created an hourly scheduled task to relaunch itself. The activity stayed on that one workstation, with no lateral movement, credential theft or malicious network traffic. It was classified as a potentially unwanted program and your team was notified. The three critical- and high-severity alerts came from software installers on WS-RAD-0032 and WS-LAB-0219 and a driver-inventory scan on SRV-APP-0008. All three were confirmed as normal activity.
30 minutes – 4 hours saved
Endpoint
Network
Identity
Email
Apps & Data
Deception Systems
Advanced Endpoint
Advanced Email
Browser (Beta)
Foundational Superpowers
Fortune 500 speed and accuracy
without the pile of parts to manage.
Nothing more to buy, integrate, or keep running. Spend what you save on something else.
Optional sources and sensors for the most protection.
Managed Deception Systems
Lures and traps for attackers, monitored natively within ReconSTORM.
Advanced Endpoint Sensor
Our best-in-class endpoint sensor works alongside or replaces your EDR.
Advanced Email Protection
First-class telemetry and operations for the world’s best email security.
Browser Protection (Beta)
Telemetry and protection that start at the browser, soon available from Recon.
AI Investigator
Agentic investigations that give your
team back hours each day.
AI that solves real problems and is available nowhere else.
| Question | MDR Alone Typical time to answer the same question by hand, pivoting between separate tools. Estimates based upon practitioner feedback. | With SIEM Typical time with a SIEM already in place, running one central query and following it up by hand. Estimates based upon practitioner feedback. | With ReconSTORM |
|---|---|---|---|
| “I have a board meeting in an hour. Summarize our security activity from the past two weeks.” | An IT team member must manually compile activity across every security and monitoring system, correlate events into a coherent narrative, and translate technical findings into language suitable for a board-level conversation. | An IT team member uses the SIEM to pull a summary of activity across the review period, identifies the most significant events, and prepares a briefing suitable for a board member. | From a real investigator run: two weeks summarized for the board, with a contained phishing email, a contained unwanted program, and three critical- and high-severity alerts confirmed as normal activity. |
| “Which endpoints have Claude installed on them?” | An IT team member queries Active Directory for computer objects, runs scripts against endpoints, and reconciles results against whatever asset records exist. | An IT team member pulls an inventory report from the EDR or MDM, filters by OS version, and identifies gaps against the expected baseline. | From a real investigator run: both installs located on the one host that had them, with versions and install paths, attributed to a single user account. |
| “Are any of our endpoints running a vulnerable version of Chrome?” | Without centralized tooling, an IT team member must run a standalone vulnerability scanner, manually scope CVE impact, and cross-reference findings with active threat detections. | An IT team member runs an installed software report, filters for vulnerable versions, identifies affected users, and checks logs for exploit attempts. | From a real investigator run: the 10 affected endpoints returned with their build numbers, ranked by asset tag, with embedded Chromium separated out as a different product. |
| “Why does Phil Connors keep getting locked out every morning?” | An IT team member must remote into each domain controller, manually filter the Windows Event Viewer, identify the caller computer, remote into that machine, and check Credential Manager. | An IT team member runs a query for Event ID 4740, identifies the source IP, checks DHCP for the hostname, and contacts the user. | From a real investigator run: both 4740 lockouts found, all 32 authentication events traced to the user’s own laptop, and brute force ruled out in favour of a stale cached credential. |
| “Has anyone clicked the link from that phishing email this morning?” | An IT team member must pull email gateway logs, identify every recipient, and cross-reference proxy or DNS logs to find outbound connections to the malicious domain. | An IT team member queries the SIEM for outbound connections to the malicious domain, correlates with email delivery logs to identify which recipients connected, and checks EDR for any post-click process activity. | <1 Minute |
| “Show me Bob Wiley’s logins for the past 48 hours. He’s supposed to be on vacation.” | An IT team member needs to identify the username, must pull event logs from individual machines or domain controllers, and know which machines to check before starting. | An IT team member needs to identify the username, run a centralized query for Event IDs 4624, 4625 and 4648, filtering by user, time and source IP. | From a real investigator run: all 105 events across 7 hosts, with the single external RDP logon cleared by enriching the address, which turned out to be the organization’s own NAT egress. |
| “Our vendor just sent us a list of attacker IPs from their breach. Have any of these ever shown up in our environment?” | An IT team member must search firewall logs, proxy logs, and endpoint telemetry separately for any historical connection to each IP on the list and correlate results across sources. | An IT team member manually extracts the IPs and formats the query to run across the SIEM for any inbound or outbound traffic involving the flagged IPs, identifies affected endpoints and users, and checks for associated process or file activity. | <1 Minute |
What do you want to learn from your data? With all your security-relevant telemetry in one place, ReconSTORM AI gives your team superpowers. | |||
The Service You Need
Expert service and real access
not included with MDR.
You’ll be backed by a team devoted to securing your organization.
Managed Security Operations
The superpowers of ReconSTORM:
- Complete environment visibility
- Extremely fast and accurate detections
- AI that can save teams hours each week
Plus, the service you need:
- 24/7 ReconSTORM provides powerful automation and AI defense. Seasoned analysts remain at the helm. investigations
- Every contract includes the kind of response you choose up front, so we can act fast when it counts. response during an attack
- When a new threat appears in the world, we’re hunting for it in your environment. We conduct dozens of hunts per week (not per year, like others). hunting for undetected threats
- You won’t have to fight through a tiered ticketing system to get answers. An expert is a direct chat or phone call away. to top-tier experts for help
- We’ll meet monthly or quarterly, as you choose, to answer questions and provide personalized, proactive guidance. org-specific guidance
Add-on or Standalone
Advanced Email Protection
- OCR, intent detection, QR decoding, and more
- Triage, expert investigation, threat hunting
- Direct user-reported email response
The Bottom Line
Complete confidence
you don’t get from MDR.
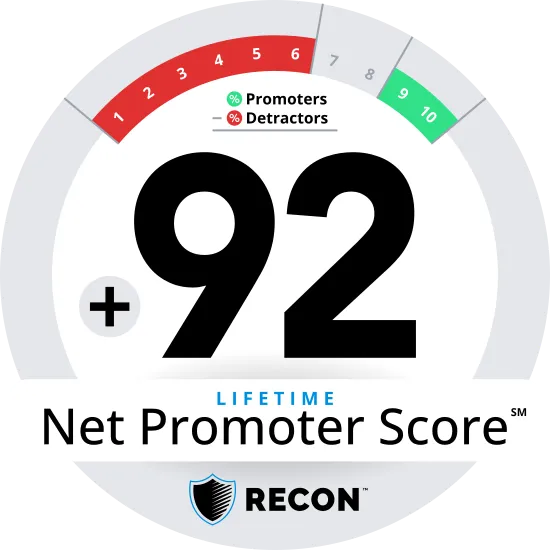
Our customers are among the happiest in the industry. Find out why.
(Compare +92 NPS to Arctic Wolf Documented on their official website in August 2026., Red Canary Most recently found published in an official press release from February 2022., eSentire Most recently found published in an official press release from February 2021.)
“Recon adds peace of mind.”
“[My favorite part is the] personal relationship with a team that feels like an extension of ours.”
“Everyone goes the extra mile to help in any way possible. Care beyond compare as I like to think about it!”
“The Recon AI tool is used daily and has made my life much easier.”
“I am at ease knowing that Recon has my back.”
“[We chose Recon] because we could tell that you’re a passionate team that is going to take good care of us.”
“This AI is a big hit with the team. It goes beyond security into actual problem solving that saves the team a lot of hours.”
“The professionalism, intelligence, and expertise from the Recon team is unmatched.”
“Assistance beyond what any other MDR can offer.”
“[The team are] very responsive and make themselves available in planning cybersecurity improvements.”
“[My favorite is] leveraging the AI investigation tool and being able to chat with a human almost instantly.”
“The data I get out of [ReconSTORM] is just invaluable.”
“Everyone we have worked with is top notch and very helpful.”
“Recon catches things VERY quickly, and it always surprises me how fast we receive alerts.”
“Recon sometimes has an investigation open before I ever see the alert from other sources.”
“[ReconSTORM] continues to evolve in ways that genuinely add value.”
“[Recon has] demonstrated a consistent level of rapid support on critical cyber needs.”

Viasat
$4.5B defense satellite network
Regional grid operator
Serves 40M+ people

Airbus
Global aerospace and defense
Farm Credit Bank of Texas
$42B regulated lender
Large-hub US airport
20M+ passengers · TSA-regulated
Southern Pine Electric
69k meters · 11 counties
Industrial water utility
50M+ gal/day to refineries
Dallas Employees’ Retirement Fund
$3.6B pension · 18,000 members
United States Cyber Command
US military cyberspace operations
Regional blood center
150+ hospitals · PHI at scale
Grocery Supply Company
4,500 retail sites · 15 states
City government
250k residents · CJIS + PCI
TML Health
~1,000 public entities · PHI
National restaurant brand
6,000+ US locations · PCI DSS

Planar
Control-room display maker
Municipal water utility
200k+ service connections
U.S. Money Reserve
High-value transactions · PCI

Verizon Media
Global media and advertising network
County government
900k+ residents · CJIS

Chambers County
Petrochemical coast · CJIS
Multi-site oncology network
50k+ patients/yr · HIPAA, 24/7
S&P 500 manufacturer
$4B+ revenue · 25+ countries
Naval Information Forces
US Navy information warfare

Fortified Data
Healthcare data · HIPAA
Large public school district
20k+ student records · FERPA
First Close
Mortgage data · GLBA
Organizations who have trusted Recon to improve their cybersecurity.
(Some customer info redacted for privacy)
Start Here
Ready to experience great cybersecurity made easy?
- 1
Say hello
NOWSchedule a quick conversation to discuss your goals and how we can help.
- 2
Select a plan
Next DayWithin a day, receive a clear, all-inclusive price to consider. See how to get much more for less.
- 3
Sleep better
ImmediatelyIntegration and monitoring begin almost immediately. You’ll see the difference fast.
- NOW
Say hello
- Next Day
Select a plan
- Immediately
Sleep better
- 1
- 2
- 3