Cross-Org Visibility for LimaCharlie
Discover how Recon InfoSec enhances security operations with LimaCharlie, offering cross-org visibility through a Prometheus exporter for unified insights.
Ben Webb
Guides
Eric Capuano ·
Archived article. Published in 2021; some details may be out of date.
In July, Eric & Whitney gave a talk titled “Breaches Be Crazy” at the SANS DFIR Summit outlining Recon’s unique approach at scaling enterprise forensic timelining.
The issue that pushed us to innovate in this area is one that most incident response teams face: acquiring, processing, and analyzing forensic data from large scale intrusions can be incredibly time consuming and difficult to scale.
While the analyzing of forensic data still requires highly skilled and experienced examiners to spend many hours finding needles in many hay stacks, we sought to significantly speed up the acquisition & processing steps.
A typical Incident Response scenario requires an examiner to take the following high-level steps:
Scope - Identify which systems are likely compromised, usually based on initial indicators (IDS/EDR/SIEM alert, etc)
Acquire - Perform forensic acquisition of scoped systems
Process - Processing of raw forensic data acquired from scoped systems
Analyze - Begin analysis of processed forensic data
Now imagine how time consuming an investigation could be for an intrusion involving 20+ systems! Without taking a long hard look at your processes, you could be wasting a lot of time and resources trying to scale traditional IR approaches. Our approach still follows this same set of steps but we’ve eliminated as much of the manual, unscalable, and time consuming pieces as possible.
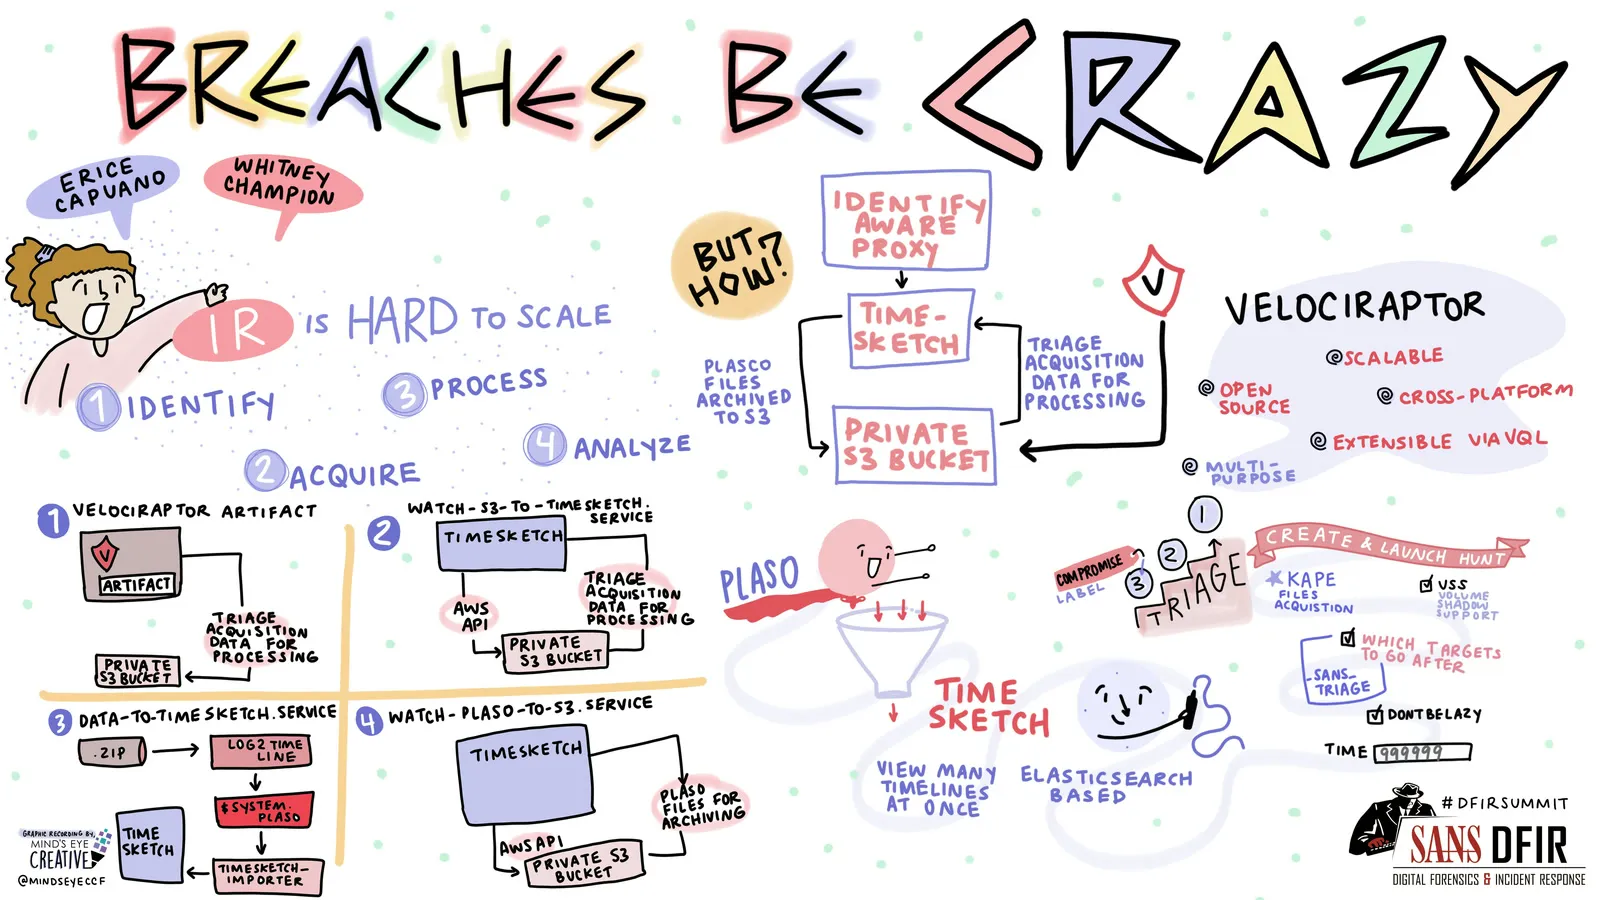
Imagine a scenario where an organization is breached and the number of compromised systems are in the double (or even triple) digits. Like many organizations, this one does not have a SIEM or log aggregation point.
Scope
Acquire
Process
Analyze
To get an idea of how fast this process can be from start to finish, we ran a benchmark with the following systems:
!SANS_Triage.tkape KAPE Files target. Generated a 4.2GB triage zip.timesketch_importer.py indexes the Plaso timeline events into Elasticsearch, and then adds the timeline to Timesketch, using this command.Check out our GitHub repo containing the custom artifacts and service files needed to build these automations and integrations.
Are you experiencing a possible breach and need expert guidance? Contact us for immediate assistance.
Discover how Recon InfoSec enhances security operations with LimaCharlie, offering cross-org visibility through a Prometheus exporter for unified insights.
Ben Webb
The recent Log4j vulnerability (CVE-2021-44228) is unprecedented in its global scope and impact.
Andrew Cook
Discover how cybercriminals trick users with fake CAPTCHA pages to deploy malware and learn effective detection techniques to safeguard your systems against these evolving threats.
Luke Rusten